 Breaking News
Director Kash Patel announced the arrest of a suspected ShinyHunters co-conspirator on Oct. 9; sources identify the suspect as Edward Dubrovsky, co-founder of Canadian cybersecurity firm CYPFER. The FBI has not publicly confirmed the link.
By Owen Barrett · October 10, 2026
 Vulnerabilities
One URL-encoded letter lets ShinyHunters walk around web application firewall rules blocking its favorite attack path — re-targeting servers that blocked the endpoint with WAFs instead of patching. Mandiant confirmed the flaw was exploited as a zero-day in May and June.
By Owen Barrett · October 10, 2026
 Research
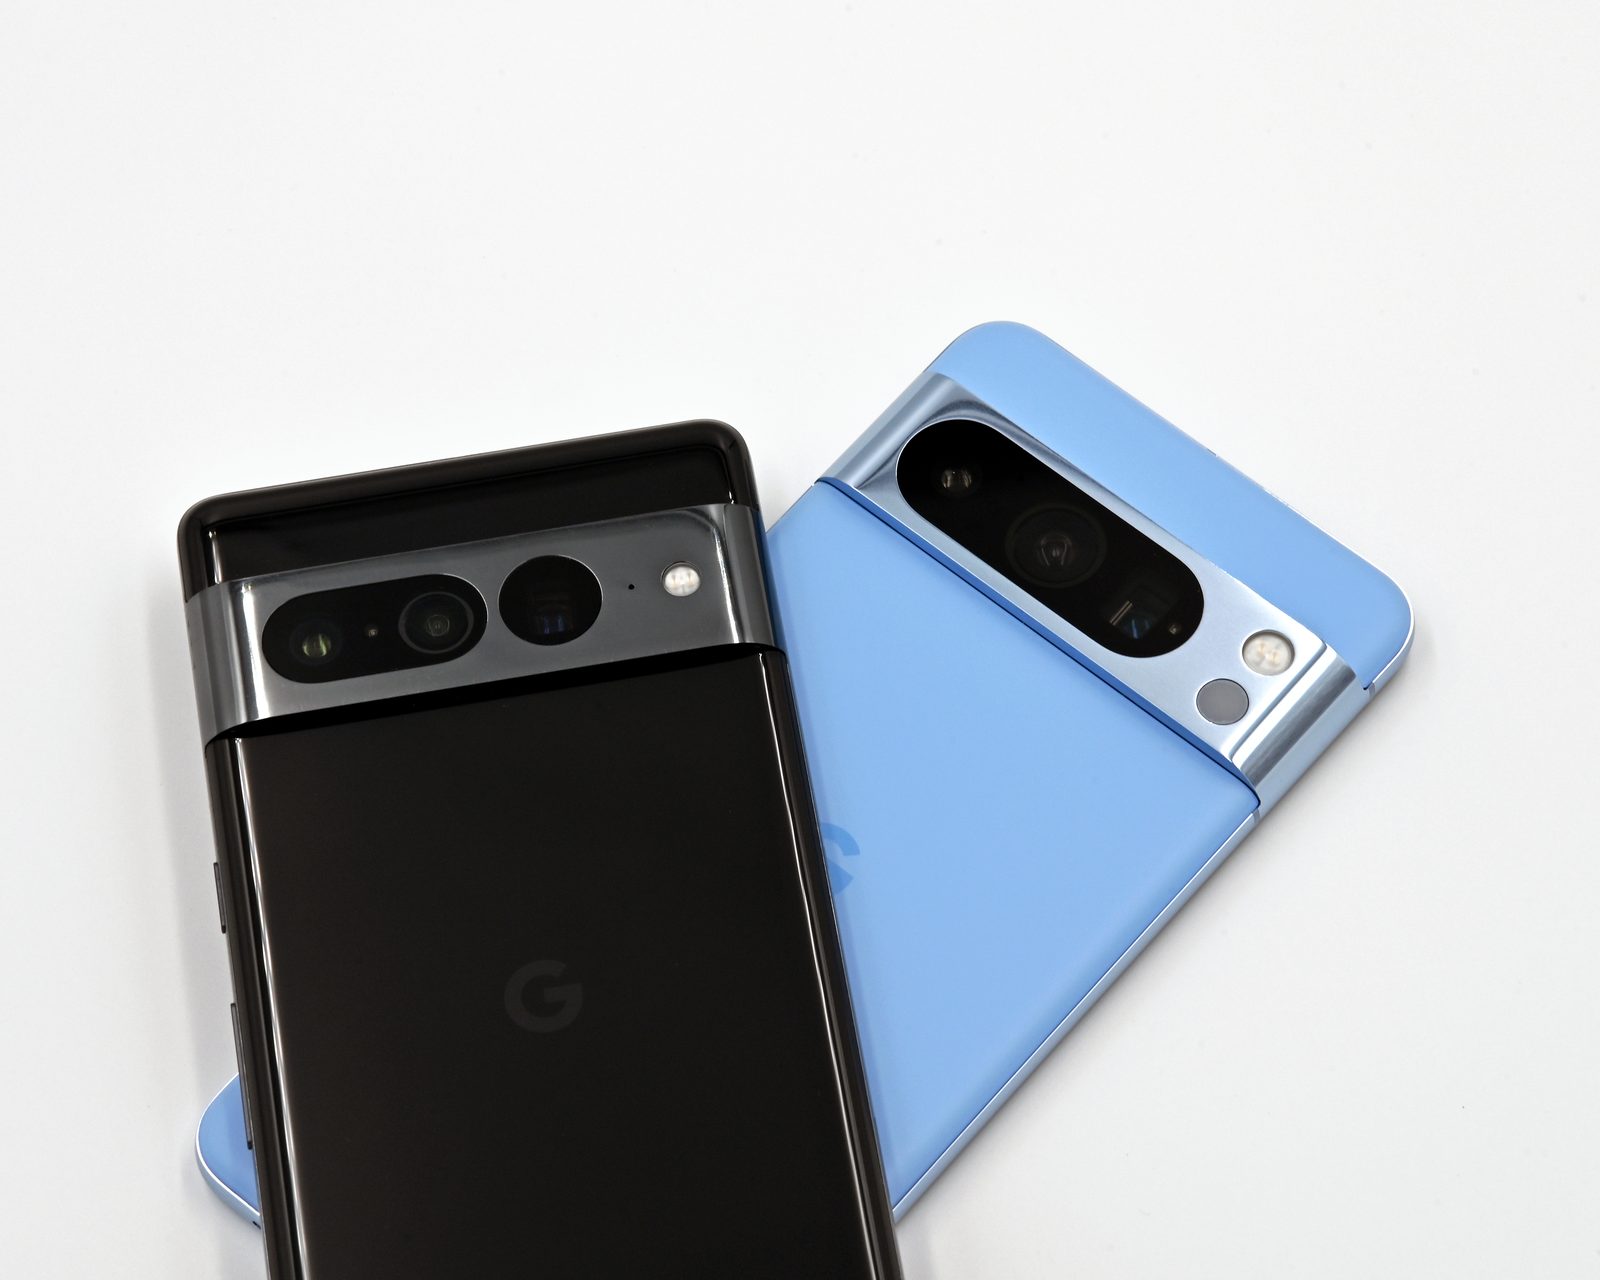
Ikotas Labs took Master of Pwn with $361,000 after a $300,000 Pixel 10 exploit chain on day three. Apple’s iPhone 17 was eligible but saw no attempts — and vendors now have 90 days to ship patches before the Zero Day Initiative discloses.
By Devon Cross · October 10, 2026
 Industry
Florida, Iowa, Montana, and Nebraska filed consumer-protection suits on Oct. 6, joining Texas in alleging the router maker misled buyers about security and its separation from China. TP-Link denies the claims — and a day later, 21 attorneys general wrote to the FCC.
By Nina Petrova · October 10, 2026
 Vulnerabilities
Three stack-based buffer overflows in the NGOAM feature let unauthenticated attackers run arbitrary code with root privileges on Nexus 3000 and 9000 Series switches. Cisco says there are no workarounds — patching is the only remediation.
By Devon Cross · October 10, 2026
 Vulnerabilities
CVE-2026-21589 lets unauthenticated attackers read files in an Atlassian application’s web root — including plaintext credentials in Crowd-integrated Jira deployments. Honeypot operators saw exploitation attempts begin within about two hours of a public proof-of-concept.
By Nina Petrova · October 10, 2026
 Breaches
The retailer says an attacker impersonated a trusted contact to steal employee login credentials, then accessed information on third-party platforms. Customer names and contact details were exposed — but not passwords or payment data. This is distinct from an earlier August breach.
By Graham Ellis · October 10, 2026
 Threats
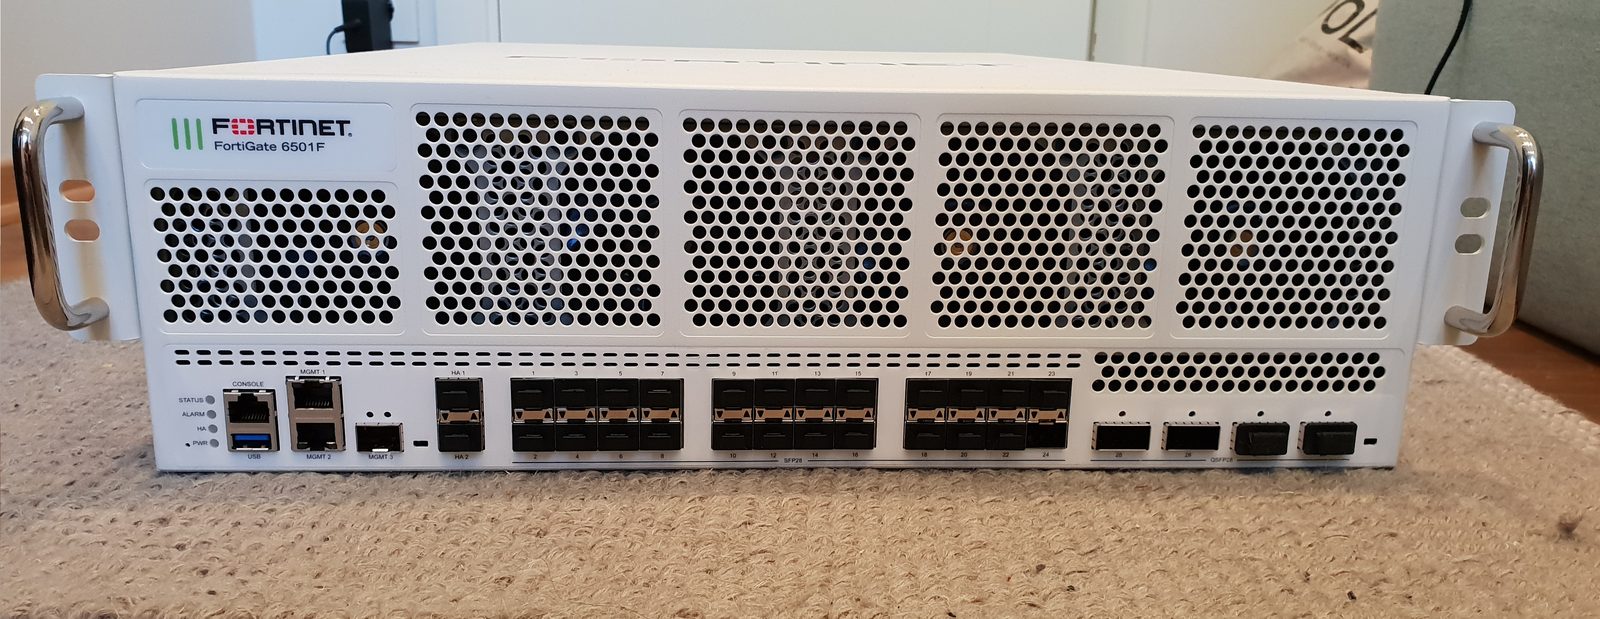
A joint advisory says the global FortiBleed campaign remains active against internet-facing Fortinet FortiGate firewalls and SSL VPN gateways — and that compromised organizations may need remediation well beyond patching and password resets.
By Graham Ellis · October 10, 2026
 Threats
A new variant of the DarkSword iOS exploit kit shrinks its on-device footprint while adding on-device keychain and crypto-wallet theft, per iVerify’s Oct 8 report — and the toolkit appears to be circulating on a second-hand commercial market.
By Tessa Quinn · October 10, 2026
 Research
A CVE is an identifier, not a verdict. Here is how IDs are assigned, what the NVD adds on top, and why the same flaw can carry two different severity scores.
By Devon Cross · October 10, 2026
 Research
An attacker’s claim is the start of an investigation, not its conclusion. This is the verification ladder HackedWire climbs before it calls a breach confirmed — worked through with the ASOS incident as the example.
By Tessa Quinn · October 10, 2026
 Research
CISA defines ransomware as malware built to encrypt files and render systems unusable — increasingly paired with data theft. This guide distills the #StopRansomware Guide into what to have ready before an incident and what to do when one lands.
By Owen Barrett · October 10, 2026
 Research
A vulnerability report starts a clock. Who gets told, how long they get, and when the details go public — the rules that turn private findings into patched systems.
By Nina Petrova · October 10, 2026